← All projects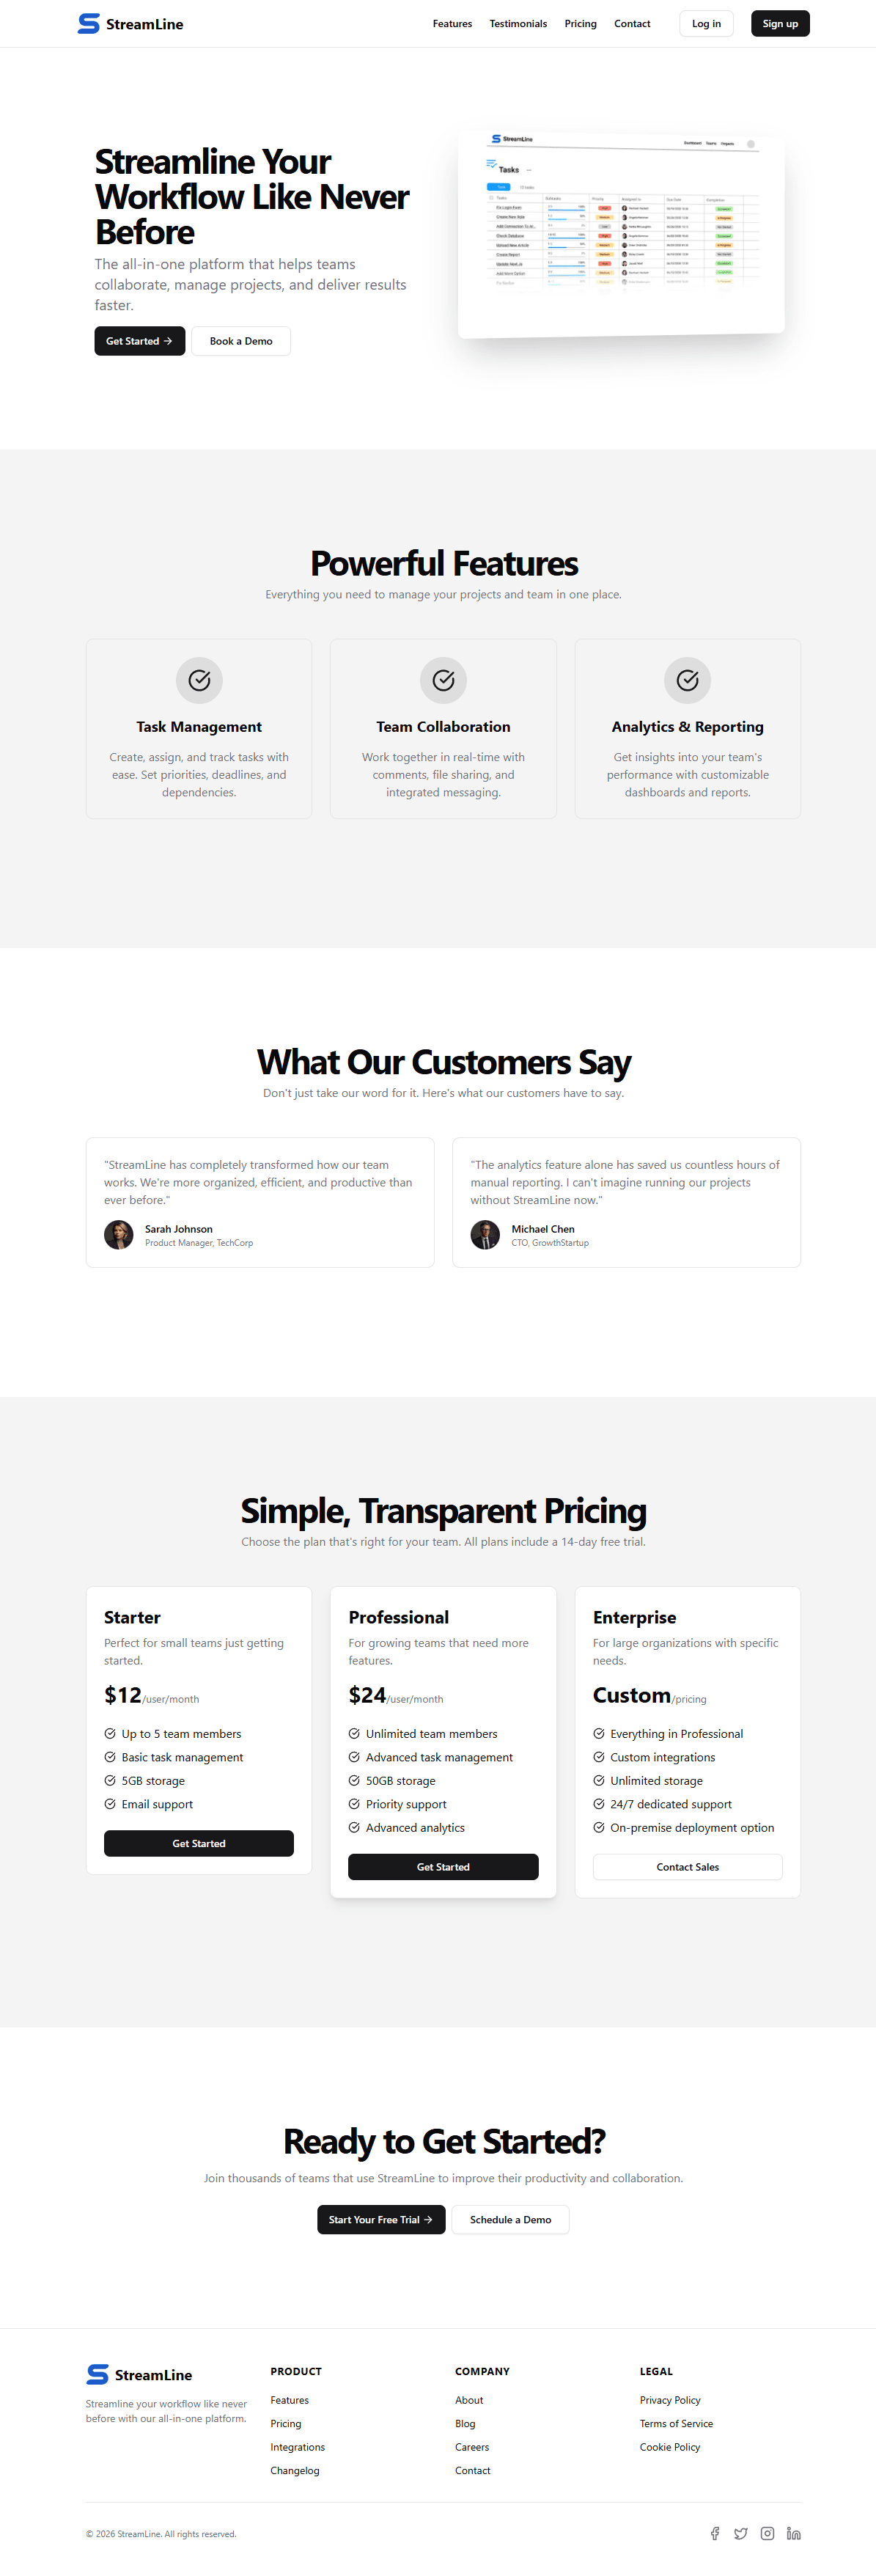
Case Study
StreamLine
A CTF to practice pentesting with some simple vulnerabilities and privilege escalation.
2025Next.jsTailwindCSSTypeScriptPostgreSQLVercelSEO
Why I built it
I've wanted to build a CTF (Capture the Flag) challenge for a while to practice penetration testing and deepen my understanding of security vulnerabilities. To that end, I developed an application that simulates an insecure SaaS platform with various security flaws and misconfigurations. The objective is to gain administrative privileges by exploiting the application's vulnerabilities and capture all the hidden flags in the format flag{...}.
The process
Studying about vulnerabilities
I've spent some time learning about security vulnerabilities through platforms such as TryHackMe and picoCTF, as well as online courses.
Creating the application
I initially developed the application with security as a priority, aiming to prevent unintended vulnerabilities while retaining only those deliberately introduced for the CTF. This required additional research into Next.js CVEs, particularly given the number of vulnerabilities being disclosed during development. One that caught my attention was CVE-2025-29927, which was disclosed around the same time I was building the CTF.
Discovering vulnerabilities
Before releasing the CTF, I needed to verify that the vulnerabilities worked as intended and that all the flags could be found. I also tested how easy it was to identify and exploit each vulnerability, adjusting the difficulty where necessary to ensure that other participants could complete the challenge without too much difficulty.
Gallery
Preview
What it improved
Thanks to this project, I learned more about penetration testing and discovered an amazing community of people who took on the challenge and tried to solve it.
- Penetration Testing
- OWASP
- Privilege Escalation
- CyberSecurity
- Capture The Flag
- CVE-2025-29927